Authentication
A familiar place to sign in.
Connect local accounts, OIDC, SAML, or LDAP. Add the login portal that suits your applications.
Explore the portal (opens in a new tab)Authentication + authorization for Caddy
Give your applications a place to sign in.
Decide who gets through.
AuthCrunch connects your identity providers, login portal, and access policies at the edge. Built for Caddy. Open source from the start.
Ready-to-run distribution Your infrastructure
Identity meets access
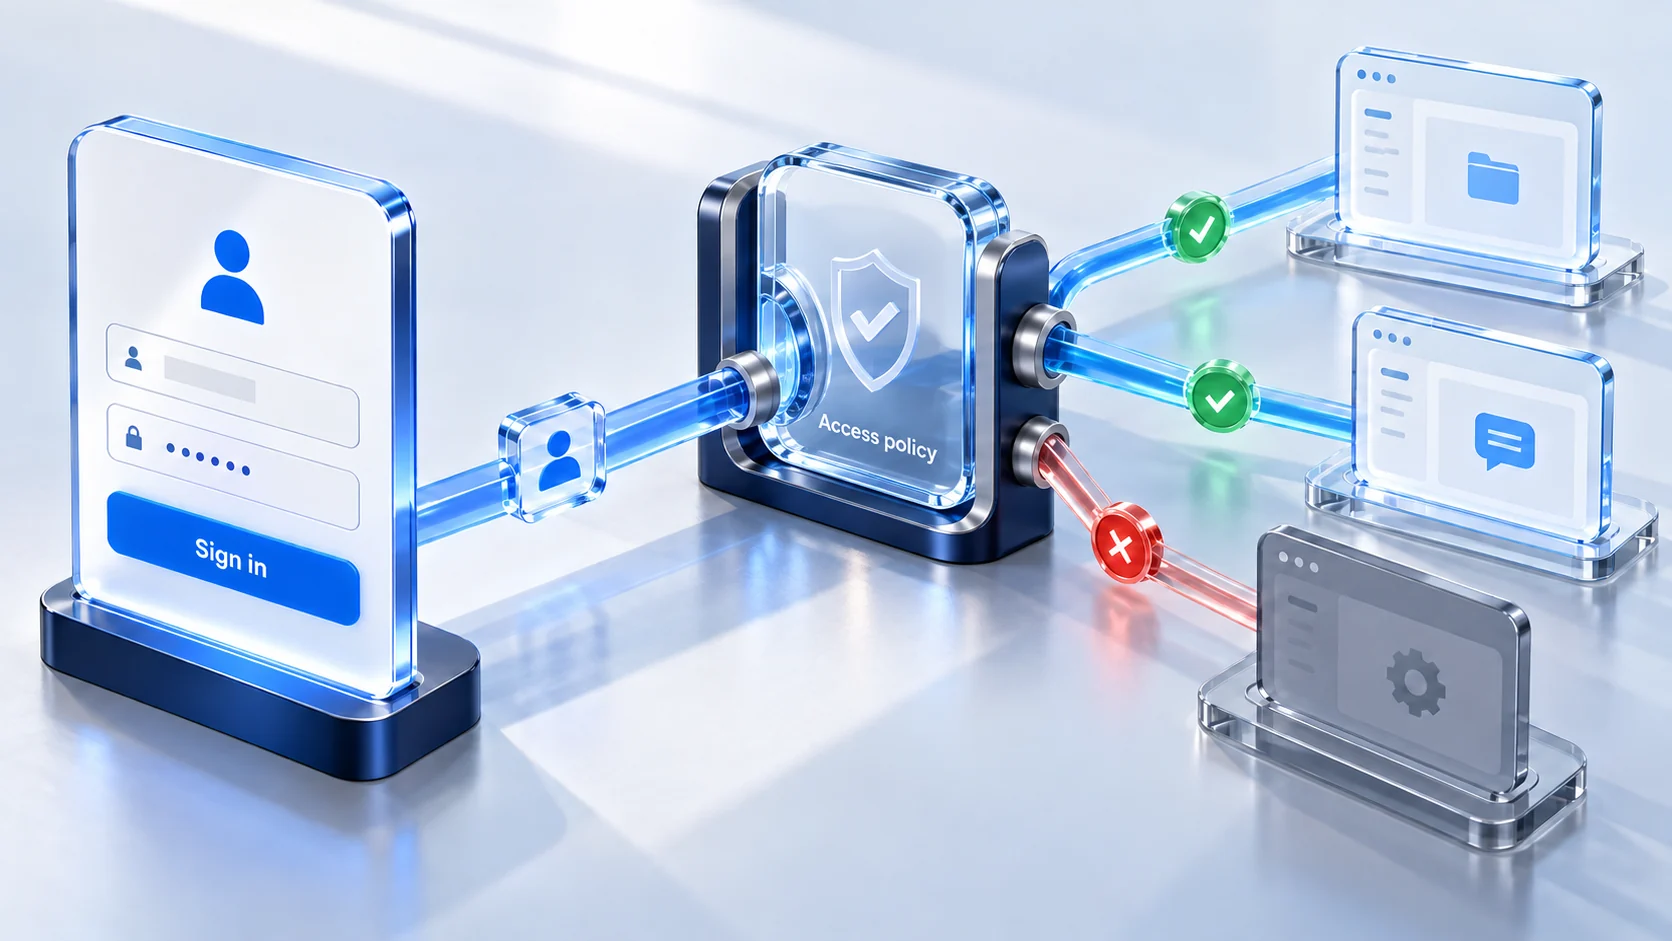
Bring the pieces together at your application’s front door. Keep the decisions in your hands.
Authentication
Connect local accounts, OIDC, SAML, or LDAP. Add the login portal that suits your applications.
Explore the portal (opens in a new tab)Authorization
Turn identity and roles into application access. Define the policy at the routes you protect.
Understand access policies (opens in a new tab)Built for Caddy
Use authentication and authorization alongside Caddy’s routing, TLS, and reverse proxy.
Find the right build (opens in a new tab)See the moving parts
Signing in tells you who someone is. An access policy decides what they can do next.
Choose a visitor. Change the rule. Watch the outcome.
Try it in a real Caddy setup (opens in a new tab)Interactive explanation · no login or server requestGET /your-applicationREQUEST EXPLORER01 / Who is visiting?
02 / Who may enter?
allow roles authp/admin authp/userAlice has a role accepted by this policy. The request reaches the app.
Build around your world
From a single service to a collection of apps.
Start with the flow that fits.
Put a portal in front of your dashboards, files, and personal tools. Choose the identities that belong in your home lab.
photos.home.exampleHTTPSOne identity. Different rules for each application.
Keep learning by doing
One Caddyfile. Two demo users.
An application you can actually protect.
Install the ready-to-run distribution and verify its modules.
Open the guide (opens in a new tab)Run the HTTPS portal locally. Follow the screenshot walkthrough.
Open the guide (opens in a new tab)See how the portal, cookies, and application policy fit together.
Open the guide (opens in a new tab)Check allowed access, denied access, and requests after logout.
Open the guide (opens in a new tab)The AuthCrunch ecosystem
AuthCrunch brings the pieces together. Each project has a clear place in the stack.
A ready-to-run Caddy distribution with caddy-security and companion plugins.
Get the distribution (opens in a new tab)The Caddy app that connects your security configuration to the authentication and authorization runtime.
Explore the Caddy app (opens in a new tab)The Go library behind the portal, identity integrations, and access policy engine.
Explore the runtime (opens in a new tab)Built in the open. Used in the real world.
Developers, infrastructure teams, and home lab builders share what AuthCrunch makes possible.
Caddy Security has greatly reduced our time to deployment while helping us unify both internal and external authentication under AWS Cognito. It integrates seamlessly with our development environments, tool deployments, and private APIs through a simple and common caddy configuration. Paul went above and beyond, working with me to ensure group and role permissions from Cognito were fully supported. A+ software.
Caddy is the primary server technology I use for personal and professional projects and AuthCrunch is my favorite way to secure it.
The Caddy security plugin allows us to use Caddy as a TLS web proxy and an authentication gateway with OAuth in one to control access to our infrastructure and operate it securely and efficiently.
Caddy Security a.k.a. AuthCrunch is a great open source addition to add authentication and authorization to Caddy. Its code is of great quality and the maintainer is very responsive and helpful to issues and questions. While these aspects make it a perfect technical choice for my organization, I also really like it on a personal level because Paul holds the values of open source software very high.
Open a pull request in authcrunch/authcrunch and add your story to ADOPTERS.md.
A commitment to open source
Paul Greenberg Maintainer, AuthCrunch
I, Paul Greenberg, as the maintainer of the open-source project AuthCrunch aka Caddy Security, hereby pledge my commitment to its continued development as a free and non-commercial project.
The project will remain licensed under an OSI-approved open-source license. You have the freedom to use, modify, and distribute the code for any purpose, including commercial applications.
About open source licenses (opens in a new tab)I will not offer any commercial products or services directly based on the codebase. This includes paid versions with additional features, support contracts, or hosted versions of the software.
The goal: a project that remains accessible and usable for everyone.
Make the next request count
Start local. Follow the request. Make the policy yours.